
Data Sovereignty
Data Sovereignty in Ad Tech: Definition, Laws and Options
Published · Last updated
Next scheduled review:
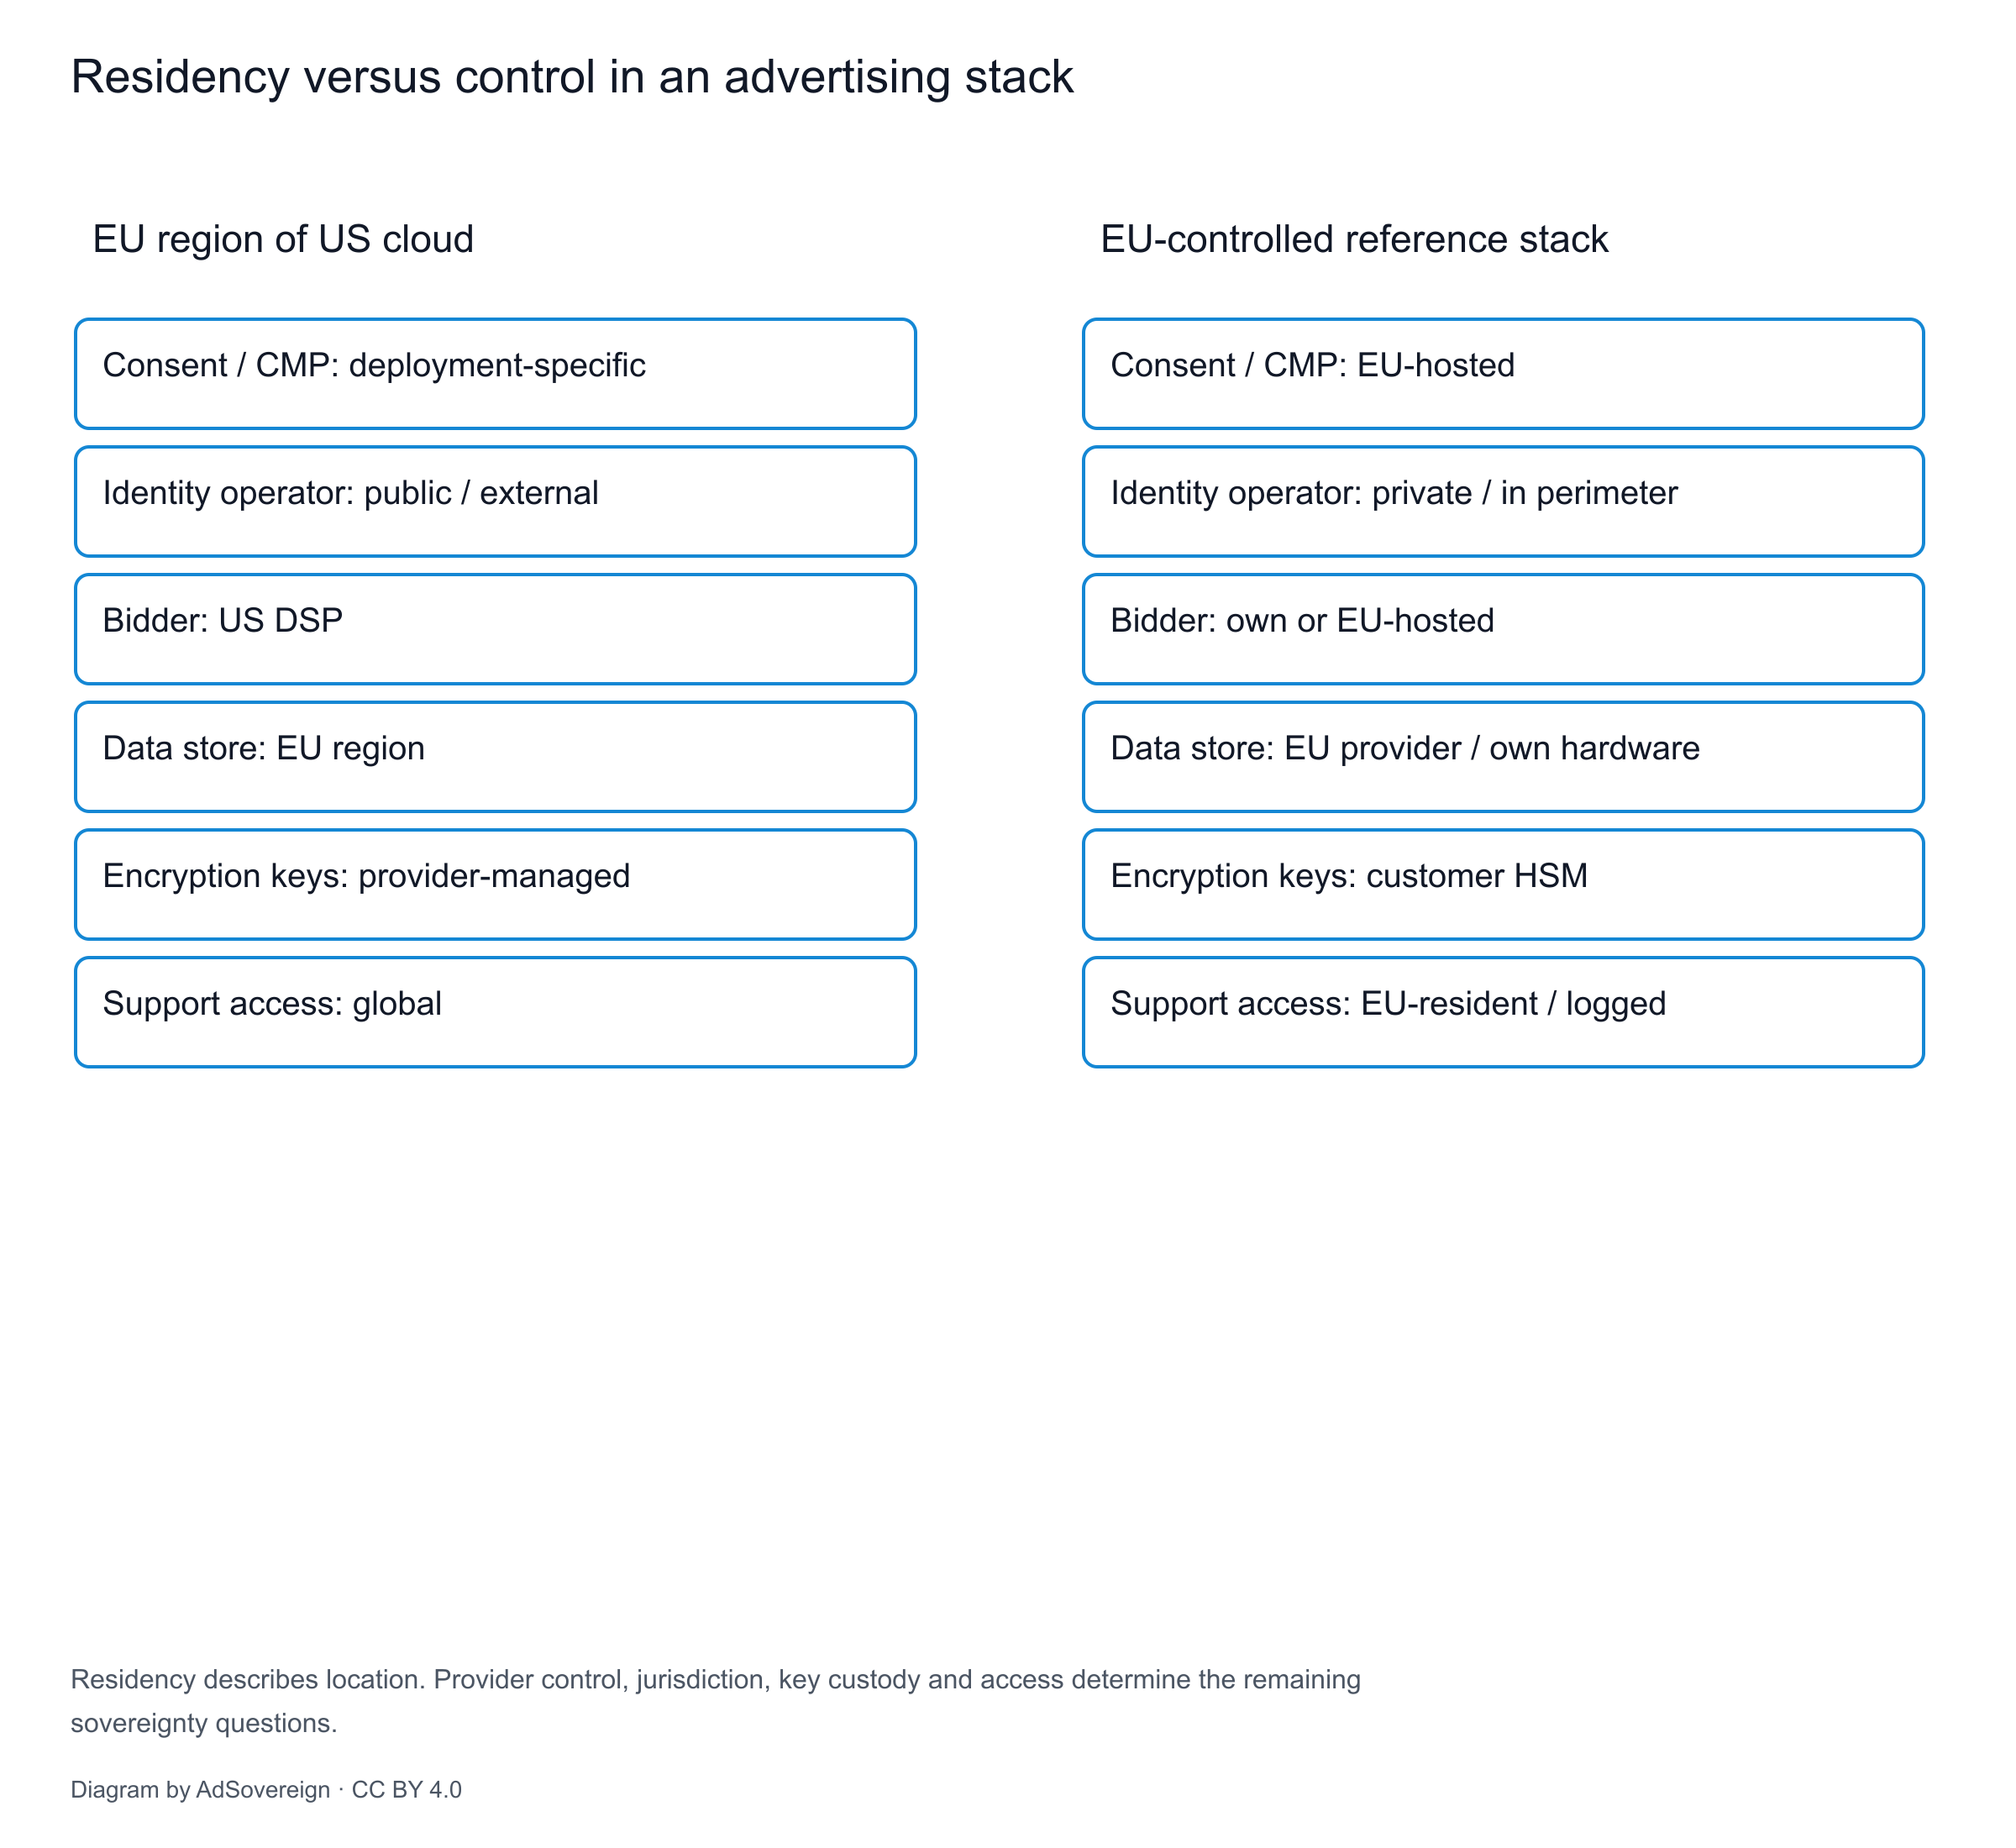
Data sovereignty concerns who can exercise legal and operational control over advertising data. Data residency describes where that data is stored. Evaluate provider jurisdiction, support access, encryption key custody, data transfers and exit rights separately. Hosting an advertising system in a particular region answers only part of the question.
Key facts
- The CLOUD Act has been law since March 2018. It lets US authorities compel a provider subject to US jurisdiction to produce data in its "possession, custody, or control" regardless of where the data is stored. The US has signed executive agreements with the UK (3 October 2019) and Australia (15 December 2021), not with the EU (US Department of Justice, CLOUD Act resources).
- EU regulators said in 2019 that a CLOUD Act order is not, by itself, a lawful basis to transfer data. The EDPB and EDPS told the European Parliament on 12 July 2019 that, absent an international agreement, such orders fall outside GDPR Article 48 (EDPB-EDPS joint response, 12 July 2019).
- The EU-US Data Privacy Framework survived its first court test, and the appeal is pending. The General Court dismissed Latombe v Commission (T-553/23) on 3 September 2025; the appeal (C-703/25 P) was lodged on 31 October 2025 and published in the Official Journal on 22 December 2025 (IAPP, 3 September 2025; OJ C/2025/6610, 22 December 2025).
- The first hyperscaler "sovereign" region is live. AWS European Sovereign Cloud reached general availability on 15 January 2026 in Brandenburg, with more than 90 services, EU-resident operations staff and German GmbH subsidiaries (Amazon, 15 January 2026).
- The EU is writing sovereignty into law and procurement. The Data Act has applied since 12 September 2025 and bans cloud switching charges from 12 January 2027 (Regulation (EU) 2023/2854, Article 29). The Commission proposed the Cloud and AI Development Act on 3 June 2026 (Wilson Sonsini, 5 June 2026).
- Ad tech is already being fined for where data goes. The Irish DPC fined Meta €1.2 billion on 22 May 2023 for EU-US transfers (DPC, 22 May 2023). The Norwegian DPA fined Xandr €8.6 million for real-time bidding with Grindr users' data in a decision of 2 October 2026 (EDPB, 16 October 2026).
Definition
Data sovereignty is the legal and operational authority over data, including jurisdiction, access, processing and the ability to enforce or change those arrangements.

Diagram by AdSovereign, CC BY 4.0.
Evaluate the workflow
For decades, advertising technology operated on a simple premise: centralize data, monetize at scale, and let platforms manage the complexity. But as privacy regulations tighten and data breaches mount, enterprises are asking a fundamental question: Who really owns our advertising data?
The End of Shared Data Economies
The walled gardens of Google, Facebook, and Amazon built empires on shared data economies. Advertisers traded control for reach, surrendering their customer insights, bidding strategies, and performance metrics to black-box platforms. The cost? Invisible data leakage, algorithmic dependency, and zero transparency into how their ad dollars actually performed.
The Data Sovereignty Imperative
Data sovereignty means complete ownership and control over where data resides, who accesses it, and how it's processed. In advertising, this translates to on-premise RTB infrastructure where every impression, bid, and audience segment stays within your firewall, not leased to a SaaS provider who monetizes your insights.
From Cloud DSPs to Data Independence
Cloud-based Demand-Side Platforms (DSPs) promise convenience: plug-and-play bidding, managed infrastructure, and "enterprise-grade" security. But beneath the surface, they extract three hidden costs:
Legal Frameworks: GDPR, CCPA, and the Compliance Advantage
Regulatory frameworks are accelerating the shift to data sovereignty. Here's why on-premise infrastructure is becoming the only compliant choice:
GDPR (General Data Protection Regulation)
Requires data minimization, purpose limitation, and explicit consent. SaaS DSPs process data in multi-tenant environments where isolation is logical, not physical. On-premise systems provide air-gapped control, no shared databases, no cross-client data exposure.
SOC2 Type II & ISO 27001
Enterprise clients demand proof of security controls. Cloud DSPs provide "shared responsibility" models where you inherit their risks. On-premise infrastructure lets you own the entire compliance stack, from network segmentation to encryption at rest.
Compliance Cost Comparison (Annual)
| Requirement | Cloud DSP | On-Premise |
|---|---|---|
| Data Breach Risk | High (shared infra) | Low (isolated) |
The Competitive Advantage of Data Sovereignty
- Algorithmic IP Protection: Your bidding strategies and audience models remain proprietary, not shared with competitors through the same platform.
- M&A Due Diligence: When private equity evaluates your company, owned infrastructure is an asset. Rented SaaS is a liability.
Real-World Impact: Finance AdTech Compliance
GDPR ComplianceAnnual SavingsData Breach Risk→ Read Full Case StudyThe Path Forward: Taking Control
The shift to data sovereignty isn't theoretical, it's happening now. Retailers like Walmart and Target are building on-premise retail media networks. Banks are deploying private ad exchanges for compliant customer acquisition. Telecom providers are monetizing first-party data without cloud intermediaries.
The question isn't whether to adopt data sovereignty. It's whether you'll lead the transition or scramble to catch up.
Take Back Control of Your Advertising Data
Download our comprehensive Data Sovereignty Playbook to learn how on-premise RTB delivers compliance, cost savings, and competitive advantage.
Download Data Sovereignty Playbook →Read the current references
Read the data sovereignty guide for the broader decision framework.
FAQ
What is the difference between data residency and data sovereignty? Residency is where data is stored and processed. Sovereignty is which jurisdiction can compel access to it, which depends on who controls the provider, who holds the keys and who has privileged access. An EU region of a US cloud gives residency. The CLOUD Act, enacted in March 2018, lets US authorities reach data a US-controlled provider holds anywhere (US DOJ), so residency alone does not give sovereignty.
Does the CLOUD Act apply to data stored in the EU? Yes, if the provider is subject to US jurisdiction. 18 U.S.C. § 2713 covers data in a provider's "possession, custody, or control" regardless of location. The provider can only move to quash on comity grounds if a "qualifying foreign government" is involved, and the only such agreements are with the UK (3 October 2019) and Australia (15 December 2021) (US DOJ). EU regulators said on 12 July 2019 that such an order is not a lawful transfer basis under GDPR Article 48 (EDPB-EDPS).
Is the AWS European Sovereign Cloud immune to the CLOUD Act? AWS has not claimed that. Its 15 January 2026 announcement describes EU-resident operations, German GmbH entities, an EU advisory board and "zero operational control outside of EU borders", and does not mention the CLOUD Act (Amazon, 15 January 2026). The entities are Amazon-owned. Whether that structure defeats a US order is untested. Treat it as reduced, not eliminated, legal exposure.
Is the EU-US Data Privacy Framework still valid in 2026? Yes. The General Court upheld it on 3 September 2025 in Latombe v Commission (T-553/23). An appeal to the Court of Justice (C-703/25 P) was lodged on 31 October 2025 and is pending (OJ C/2025/6610, 22 December 2025). Companies that rely on DPF certification should keep SCCs or BCRs ready as a fallback.
Can an EU company legally send bid requests to a US DSP? It can, with a lawful basis for each data element, a transfer mechanism for the recipient and data minimization. Since 7 March 2024 the TC String itself counts as personal data when linked to an IP address (CJEU C-604/22), and the Norwegian DPA's October 2026 Xandr decision shows that platforms in the chain are joint controllers (EDPB, 16 October 2026). The sovereignty question is separate: once the request is in the DSP's logs, US law reaches it. Stripping identifiers for non-EU buyers or routing EU supply to EU-hosted buyers avoids both problems.
How this works on owned infrastructure
AdSovereign provides an enterprise RTB stack for deployment inside a customer’s own infrastructure. Use the architecture to map the relevant components, the security controls to evaluate access and data boundaries, and the pilot to define a bounded evaluation. Compare the operating responsibilities and commercial terms against your own requirements. Infrastructure control does not establish demand access, legal permission or a measured performance improvement on its own.
Sources
- US Department of Justice, "CLOUD Act Resources" (March 2018 enactment; UK agreement 3 October 2019; Australia agreement 15 December 2021). https://www.justice.gov/dag/cloudact
- Congress.gov, H.R. 4943, Clarifying Lawful Overseas Use of Data Act (115th Congress). https://www.congress.gov/bill/115th-congress/house-bill/4943
- EDPB and EDPS, "Joint response to the LIBE Committee on the impact of the US CLOUD Act on the European data protection framework" (12 July 2019). https://www.edpb.europa.eu/our-work-tools/our-documents/letters/edpb-edps-joint-response-libe-committee-impact-us-cloud-act_en
- Regulation (EU) 2016/679 (GDPR), Articles 44 to 49. https://eur-lex.europa.eu/eli/reg/2016/679/oj
- CJEU, Case C-311/18, Data Protection Commissioner v Facebook Ireland and Schrems (16 July 2020). https://eur-lex.europa.eu/legal-content/EN/TXT/?uri=CELEX:62018CJ0311
- EDPB, "Recommendations 01/2020 on measures that supplement transfer tools", final version (18 June 2021). https://www.edpb.europa.eu/our-work-tools/our-documents/recommendations/recommendations-012020-measures-supplement-transfer_en
- Commission Implementing Decision (EU) 2023/1795, EU-US Data Privacy Framework (10 July 2023). https://eur-lex.europa.eu/eli/dec_impl/2023/1795/oj
- IAPP, "European General Court dismisses Latombe challenge, upholds EU-US Data Privacy Framework" (3 September 2025). https://iapp.org/news/a/european-general-court-dismisses-latombe-challenge-upholds-eu-us-data-privacy-framework
- Hunton, "EU's General Court Confirms Adequacy of EU-U.S. Data Privacy Framework" (3 September 2025). https://www.hunton.com/privacy-and-information-security-law/eus-general-court-confirms-adequacy-of-eu-u-s-data-privacy-framework
- Hogan Lovells, "Transatlantic data transfers: EU General Court upholds Data Privacy Framework" (3 September 2025). https://www.hlc.com/en/publications/transatlantic-data-transfers-eu-general-court-upholds-dat-privacy-framework
- Official Journal of the EU, C/2025/6610, Case C-703/25 P, Latombe v Commission, appeal brought 31 October 2025 (22 December 2025). https://eur-lex.europa.eu/eli/C/2025/6610/oj
- Amazon, "AWS Launches AWS European Sovereign Cloud and Announces Expansion Across Europe" (15 January 2026). https://press.aboutamazon.com/aws/2026/1/aws-launches-aws-european-sovereign-cloud-and-announces-expansion-across-europe
- Microsoft, "Microsoft completes landmark EU Data Boundary" (26 February 2025). https://blogs.microsoft.com/eupolicy/2025/02/26/microsoft-completes-landmark-eu-data-boundary/
- Microsoft News Center Spain, "Microsoft presenta nuevas soluciones de Nube Soberana para las organizaciones europeas" (16 June 2025). https://news.microsoft.com/es-es/2025/06/16/microsoft-presenta-nuevas-soluciones-de-nube-soberana-para-las-organizaciones-europeas/
- European Cloud, "Microsoft cannot guarantee data sovereignty" (24 July 2025, updated 2 December 2025; secondary report of French Senate testimony). https://european.cloud/2025/07/microsoft-cannot-guarantee-data-sovereignty/
- Google Cloud, "Advancing digital sovereignty on Europe's terms" (11 October 2022). https://cloud.google.com/blog/products/identity-security/advancing-digital-sovereignty-on-europes-terms
- Google Cloud documentation, "Sovereign Controls by Partners overview" (undated, retrieved 17 October 2026). https://docs.cloud.google.com/sovereign-controls-by-partners/docs/overview
- Google Cloud, "Sovereign Cloud" (undated). https://cloud.google.com/sovereign-cloud
- OVHcloud, "SecNumCloud" (Managed VMware vSphere qualified December 2020; SNC Cloud Platform September 2026). https://www.ovhcloud.com/en/enterprise/certification-conformity/secnumcloud/
- STACKIT, homepage (undated). https://stackit.com/en/
- Scaleway, homepage (undated). https://www.scaleway.com/en/
- Regulation (EU) 2023/2854 (Data Act), Articles 29, 32 and 50. https://eur-lex.europa.eu/eli/reg/2023/2854/oj
- The Register, "Big clouds scramble as EU Data Act brings new data transfer rules" (10 September 2025). https://www.theregister.com/2025/09/10/big_clouds_scramble_over_eu/
- Regulation (EU) 2022/1925 (Digital Markets Act), Articles 5(2), 5(9), 5(10), 6(8). https://eur-lex.europa.eu/eli/reg/2022/1925/oj
- European Commission, "Commission finds Apple and Meta in breach of the Digital Markets Act", IP/25/1085 (23 April 2025). https://ec.europa.eu/commission/presscorner/detail/en/ip_25_1085
- Wilson Sonsini, "European Commission Publishes Proposal for Act to Reduce Reliance on Foreign Cloud and AI" (5 June 2026). https://www.wsgrdataadvisor.com/2026/06/european-commission-publishes-proposal-for-act-to-reduce-reliance-on-foreign-cloud-and-ai/
- IAPP, "A view from Brussels: To be sovereign or not to be" (25 April 2024). https://iapp.org/news/a/a-view-from-brussels-to-be-sovereign-or-not-to-be
- Agenda Digitale, "ENISA e certificazione cloud: costruire uno standard di sicurezza europeo" (16 March 2026; EUCS status and Commission Cloud Sovereignty Framework of 20 October 2025). https://agendadigitale.eu/sicurezza/enisa-e-certificazione-cloud-costruire-uno-standard-di-sicurezza-europeo
- Irish Data Protection Commission, "Data Protection Commission announces conclusion of inquiry into Meta Ireland" (22 May 2023). https://www.dataprotection.ie/en/news-media/press-releases/Data-Protection-Commission-announces-conclusion-of-inquiry-into-Meta-Ireland
- CNIL, "Sanctions issued by the CNIL" (list; Criteo 15 June 2023). https://www.cnil.fr/en/sanctions-issued-cnil
- Privacy Laws & Business, "CNIL fines Google €325 million and Shein €150 million" (4 September 2025). https://www.privacylaws.com/news/cnil-fines-google-325-million-and-shein-150-million/
- EDPB, "Norwegian DPA fines Xandr EUR 8 600 000 for unlawful processing of personal data" (16 October 2026; decision 2 October 2026). https://www.edpb.europa.eu/news/norwegian-dpa-fines-xandr-eur-8-600-000-for-unlawful-processing-of-personal-data_en
- CJEU, Case C-604/22, IAB Europe v Gegevensbeschermingsautoriteit (7 March 2024). https://eur-lex.europa.eu/legal-content/EN/TXT/?uri=CELEX:62022CJ0604
- IAB Tech Lab, OpenRTB 2.6 specification (GitHub). https://raw.githubusercontent.com/InteractiveAdvertisingBureau/openrtb2.x/main/2.6.md
- IAB Europe, "Transparency & Consent Framework" (TCF v2.3; adoption deadline 28 February 2026). https://iabeurope.eu/transparency-consent-framework/
- EUID documentation, "Public and Private Operators" (retrieved 17 October 2026). https://euid.eu/docs/ref-info/ref-operators-public-private
- PPC Land, "The Trade Desk integrates Utiq's telco identity signals across EMEA" (1 June 2026; Utiq figures as of 15 November 2025). https://ppc.land/the-trade-desk-integrates-utiqs-telco-identity-signals-across-emea/
- Clifford Chance, "EU e-Evidence Regulation and Directive: What it means for e-commerce platforms" (August 2026). https://www.cliffordchance.com/insights/resources/blogs/regulatory-investigations-financial-crime-insights/2026/08/eu-e-evidence-regulation-and-directive-what-it-means-for-e-commerce-platforms.html
Changelog
October 18, 2026: aligned the approved search title and heading; retained the original publication date.
October 17, 2026: updated search phrasing, source-linked reference context, author and dates. Withheld numerical claims without inline sources.